Is GMGN Safe? Custody, Private Keys, and What You Actually Control
Table of Contents
- What is the one fact that decides everything else?
- Four places GMGN's own material says it holds the key
- The contradiction, quoted from both sides
- What does "cannot exit" cost you in practice?
- What withdrawal holds does GMGN's documentation publish?
- Does GMGN front-run its own users?
- Where the money that actually disappears goes
- The legal picture is thinner than you would expect
- So, is GMGN safe?
"Is GMGN safe" is usually answered with a verdict. That is the wrong shape of answer. This research found no verified compromise of GMGN's own infrastructure as of 6 August 2026, and GMGN has publicly paid compensation after users were harmed. Its documentation also says you cannot export the private key to the wallet it generates for you, which is a different kind of risk that most reviews skip, because it sits on a documentation page whose title says the opposite.
This page lays out what GMGN's documents say, where they describe the same thing in incompatible ways, and what that means for how much money you should keep there. Nothing here is financial, legal or tax advice.
GMGN's wallet documentation says private key export is prohibited on every chain, including wallets you imported yourself, and describes no seed phrase. Its Terms of Service says you retain control of your keys, while its documentation, its Agent API page and its bug bounty each describe key handling you cannot reach. This page does not resolve which of those is legally correct. The practical read is a hot trading account you cannot exit by key. Keep trading capital in it and move profits to a wallet whose keys you actually hold.
What is the one fact that decides everything else?
You cannot export a private key from a GMGN wallet on any chain it supports, including a wallet you imported yourself. GMGN's own wallet documentation is unambiguous about it:
For the safety of user wallet funds, GMGN all chains ( SOL chain / EVM chain / Tron chain ) are prohibited from exporting private keys; Wallets imported from outside also can't export private keys.
That is verbatim from GMGN's TG wallet documentation, and the same sentence appears in bold on the wallet connection page.
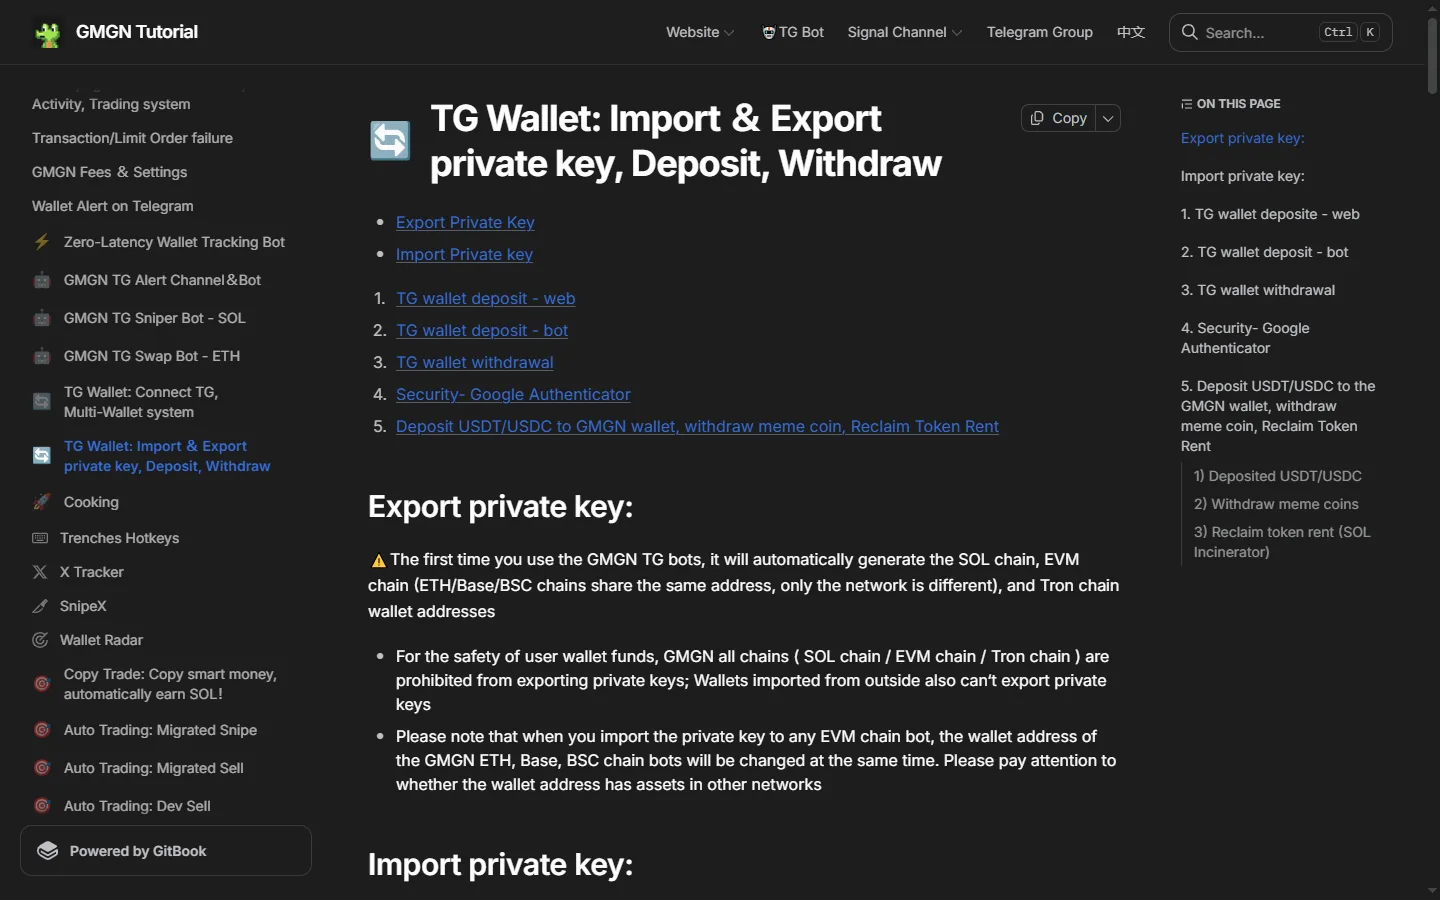
Read the second clause again. Wallets you generated yourself, elsewhere, and imported into GMGN also cannot be exported. Import is a one-way door.
Export was disabled around 19 March 2025. Co-founder Haze gave the rationale at the time: to eliminate security risks and protect asset safety, the wallet generated by GMGN does not support exporting private keys, a change prompted by thefts that happened after users exported their keys (Gate News). That rationale is real. Clipboard-stealing malware harvesting a plaintext key out of a Telegram chat was a live problem, and removing the key from the client removes that attack surface.
It also removes every user's exit path. Both things are true at once.
Warning
The documentation page that announces the ban is still titled "TG Wallet: Import & Export private key, Deposit, Withdraw", and an older sniper bot page still says "You can import and export private keys and change wallets here" (GMGN sniper bot docs). That stale title is why dozens of third-party guides still walk you through exporting a GMGN key. You will not find the button. The current documentation describes the capability as prohibited, not relocated.
Four places GMGN's own material says it holds the key
The export ban on its own could be read as a UI restriction rather than a custody statement. It is not the only signal.
| Where | What GMGN says | What it implies |
|---|---|---|
| Wallet docs | All chains are prohibited from exporting private keys, including imported wallets | The key exists somewhere you cannot reach |
| Agent API docs | Adopts the GMGN hosted wallet architecture where private keys are not stored locally | Server-side key handling, stated as a feature |
| Phantom login | GMGN will create a multi-chain custodial wallet account based on your Phantom wallet | GMGN's documentation uses the word custodial here |
| Bug bounty | Top tier covers unauthorized access to GMGN wallets, funds, or private keys | The published scope names GMGN wallets, funds and private keys |
The Agent API language comes from GMGN's Agent API page. The Phantom quote is from the multi-wallet documentation, which also notes that connecting Phantom generates fresh addresses on each chain rather than trading from your Phantom address. The bounty tier is from the GMGN Vulnerability Bounty Program, which pays up to 1,000,000 USDT in its "Extreme" band for vulnerabilities "potentially leading to major business disruptions or unauthorized access to GMGN wallets, funds, or private keys." That is GMGN's own description of the scope it will pay to have tested.
No GMGN document we read on 6 August 2026 describes MPC, threshold signing, secure enclaves or any other architecture that would let GMGN sign a transaction without a key sitting on its side. We could not confirm the architecture either way, because GMGN does not publish it. What is on the record is the list above.
The contradiction, quoted from both sides
Now put the documentation next to the contract. GMGN's Terms of Service, at gmgn.ai/static/tos.html, section 3.3, says this:
...while maintaining control over your private keys. The TG Bot functions as an interface that allows you to interact with your own wallet created by GMGN. When you transfer funds to this wallet, you retain control over your private keys and assets.
Set that against the documentation sentence at the top of this page. One document says users retain control over their private keys. The other says users are prohibited from exporting them on every chain supported. Both were live when we read them on 6 August 2026. Both are published by GMGN. Which one governs is a question for a lawyer reading the whole agreement, not for a guide, so we are not answering it here.
The Terms go further with a disclaimer written in capitals, and it carries a qualifier worth reading slowly:
GMGN CANNOT INITIATE A TRANSFER OF ANY OF YOUR CRYPTOCURRENCY OR DIGITAL ASSETS OR OTHERWISE ACCESS YOUR DIGITAL ASSETS IN YOUR OWN WEB3 WALLETS
Note the closing words, "in your own web3 wallets." The sentence does not say "in your GMGN wallet," and we are flagging the wording rather than telling you what it means. GMGN's safety documentation states the point more broadly in plain text, saying GMGN "does not perform any operations on the user's wallet, and we do not have the ability to transfer any user's wallet balance." Nothing in this research contradicts that statement. Read the clause and the documentation side by side, and take advice if the difference matters to your situation.
Info
To be explicit, because this niche is full of accusations: no report of GMGN taking user funds turned up in this research as of 6 August 2026. We found no verified compromise of GMGN's infrastructure, no front-end hijack, no supply-chain attack and no disclosed data breach. The criticism on this page is about a custody model you cannot exit by key and a documentation set that describes it in incompatible ways, not about theft.
What does "cannot exit" cost you in practice?
Three consequences follow, and they are the ones that actually cost people money.
Your Telegram account is your wallet. GMGN's wallets are generated and bound at first login through Telegram, and there is no exportable key or seed phrase behind them. GMGN's documentation describes no key-based recovery path if that Telegram account is lost, banned or taken over. GMGN devotes a section of its safety tips to hardening Telegram itself, including two-step verification and blocking group invites. On this setup, the Telegram account is the weakest link in the chain, and that section is the closest thing GMGN publishes to an acknowledgment of it.
Importing to an EVM bot deletes your old address. This one is stated with an exclamation mark in the docs and is still routinely missed:
When you import a new wallet address to EVM chain bots, the old wallet address will be automatically deleted. There is no way to help you recover your assets!
The ETH, Base and BSC bots share one address, so importing a key into any of them changes all three at once (wallet docs). Anything sitting on the replaced address across those three networks is gone from your reach, and because export is banned you cannot recover it with the old key either. Solana behaves differently: importing there opens the multi-wallet manager and keeps the previous wallet.
The path that keeps your keys costs you the product. You can use GMGN with a browser extension wallet through "Trade with Wallet", which leaves your keys where they already were. Doing so forfeits Anti-MEV routing and the automation suite, and creates a separate account whose data is not shared with a Telegram-wallet account (multi-wallet docs). That is the real trade: hold your own keys, or get the features people come to GMGN for. Pick knowingly. Our how to trade on GMGN walkthrough covers both paths, and connecting Telegram and funding the wallet covers the setup if you take the bot route.
If you use GMGN, use it with the risk priced in
Trade from a GMGN wallet only with capital you are prepared to leave on a platform you cannot exit by key. We earn a referral commission if you sign up through our link; GMGN pays the referrer only, so this costs you nothing and gets you nothing extra.
Open GMGNWhat withdrawal holds does GMGN's documentation publish?
Before concluding that GMGN has frozen your funds, check this list, because each of these rules is published and each of them looks like a freeze from the inside. Withdrawal was moved off the Telegram bot entirely and rebuilt on the website in March 2025, with 2FA, whitelisting and time locks added at the same time (Odaily, 25 March 2025).
| Control | Rule | What triggers the complaint |
|---|---|---|
| Where you withdraw | Website only. The Telegram bot cannot withdraw at all | Users hunt for a Withdraw button in the bot and conclude funds are frozen |
| 2FA | Google Authenticator must be bound before any withdrawal | Setup is required first, so the first attempt always fails |
| Whitelist | Transfers only go to whitelisted addresses; whitelisted addresses then bypass 2FA | A fresh destination address is simply not selectable |
| 3-hour hold | No withdrawals for 3 hours after first whitelist setup or any whitelist change | Reads as a freeze; it is a fixed cooling-off period |
| 24-hour hold | 24-hour withdrawal hold after re-binding Google Authenticator | New phone, re-bind, then a day of waiting |
| Max button | Never sends the full balance; a minimum is retained for account rent and gas | Reads as a skimmed fee, is actually rent-exemption plus gas |
Every row comes from GMGN's own withdrawal documentation. Each control raises the cost of an attack on your session, and each one also slows you down when you want to move quickly. That trade-off is the practical thing to plan around. If your withdrawal is not blocked by one of the rows above, our transaction failure guide covers the error codes that explain the rest.
Tip
GMGN recommends binding Google Authenticator with cloud sync turned off, using the "Use Authenticator without an account" option, so a compromised Google account cannot hand over every 2FA code at once. Worth doing. Worth noting too is what the documentation we read on 6 August 2026 does not describe: no passkeys, no hardware security key, no email or SMS withdrawal confirmation, no anti-phishing code and no device or session management screen. Features can exist without being documented, so treat that as a gap in the docs rather than a confirmed gap in the product.
Does GMGN front-run its own users?
The most repeated claim about GMGN is that it front-runs or sandwiches its own users. The on-chain record points firmly the other way, and this is worth getting right because it is the one place where the crowd consensus is simply wrong.
GMGN's users were the victims. In an April 2025 analysis of Solana sandwich activity, GMGN was reported as the single most sandwich-victimized app on Solana, accounting for roughly 30.8% of sandwich attack profits relative to its own activity, inside a 30-day window covering more than 260,000 attacks and about 23,600 SOL extracted across Solana trading apps (Ainvest). That report does not name the underlying dashboard, so treat the exact percentage as a reported figure rather than one we independently reproduced. The direction of the finding is what matters: GMGN's order flow was being harvested, not doing the harvesting.
GMGN's behavior fits that reading:
- In March 2025, co-founder Haze publicly pressed Solana over validators leaking transaction data to sandwich bots (AiCoin).
- In July 2025, GMGN shipped hardened MEV protection with a compensation process attached. Haze's words: "If it has been verified that MEV was enabled and you were sandwiched, we will compensate you", while conceding the protection "is not perfect" (crypto.news).
- GMGN's fee documentation ships a plain-English explanation of sandwiching and a three-tier Anti-MEV RPC selector, with the trade-off between speed and protection spelled out (fee settings docs). We break the settings down in the GMGN fees guide.
In late October 2025 GMGN was hit by a phishing wave in which a forged third-party token website drove unauthorized transactions, affecting roughly 107 users. Haze committed to 100% compensation and the funds were credited directly to affected GMGN accounts, with no claim process for users to navigate (Lookonchain, Phemex News, 28 October 2025). GMGN separately published a statement rejecting the broader "GMGN was hacked" rumors after an audit (@gmgnai).
On the accusation that gets repeated most, the reporting runs backwards. An April 2025 analysis described GMGN as the most sandwich-victimized app on Solana, inside a window covering 260,000+ attacks (Ainvest); that piece does not name its source dashboard, so the figures are reported rather than reproduced here. Its co-founder publicly pressed Solana validators over leaked transaction data, shipped anti-MEV routing with a compensation policy, and paid out. The MEV risk a GMGN user faces comes from third-party bots, and the mitigation is a setting you control.
Set against that public record, the front-running story has nothing behind it that we could find. No specific, credible allegation naming GMGN as the front-runner surfaced in this research as of 6 August 2026. Treat the claim as unsupported until someone produces transactions.
Where the money that actually disappears goes
GMGN's own support pages are the best evidence for what causes user losses, because they are essentially a catalog of what support gets asked about. From the Q&A and safety tips, the recurring causes are: device malware from clicking unknown links, Telegram installed from unofficial sources, third-party Telegram translator plugins, authorizing a fake bot, and signing a malicious approval from an airdropped NFT. GMGN's blunt summary is that these are "GMGN official can not control", and on the causes listed above that description matches what the incidents involved.
None of those causes are things the terminal screens for, which is worth separating from the checks it does run. GMGN puts a contract security panel on every token page, and its fields are about the token rather than about your device or your Telegram account: what the contract security panel screens for defines mint authority, blacklist, LP burned and honeypot from GMGN's own wording, one field at a time. A clean panel says nothing about the five causes above.
Two patterns are worth naming precisely.
Fake bot handles. Scammers register lookalike Telegram handles using a capital "I" in place of a lowercase "l", which is visually identical in most fonts (sniper bot docs). GMGN also warns never to click the ads that Telegram displays above the bot, and states that official admins never DM first and never ask for a private key.
Fake domains. A live phishing clone at app-gmgn-ai.com has its own removal guides from security vendors (PCrisk), and Bing surfaces typosquats like gmgn-tracker and gmgn-app.at in its index. On RDAP and DNS checks run 6 August 2026, the obvious TLD variants did not resolve to a GMGN site: gmgn.com was registered in 2004, before gmgn.ai existed, gmgn.org was parked for sale on Afternic, gmgn.net returned a server error and gmgn.app was an empty deploy. Verify the address bar rather than assuming a variant belongs to GMGN. The same problem exists on the app stores, where a search is not a verification step; is there a GMGN mobile app records the two listings gmgn.ai/app itself links to and the developer and seller names on each.
| Real | What it is |
|---|---|
| gmgn.ai | The app. Everything else on this list is a subdomain or a support surface |
| docs.gmgn.ai | Official documentation, and the source of most quotes on this page |
| papi.gmgn.ai | API host |
| www.gmgn.cc | Official chart embeds, plus the info@gmgn.cc support address. Not a typosquat |
| x.com/gmgnai | The only account GMGN tells users to verify the real Telegram group against |
| t.me/gmgnai | Official community group |
| security@gmgn.ai | Security contact, alongside the HackenProof bounty program |
Treat anything outside that list as unofficial until you can verify it, including the gmgn.io, gmgn.com, gmgn.net, gmgn.org and gmgn.app variants, none of which served a live GMGN site when we checked them on 6 August 2026. On the Telegram side, GMGN's alert channel documentation states the reason for its own setup in one line: "To avoid scam ads shown in public channels, the GMGN Team has switched official channels to private channels."
The legal picture is thinner than you would expect
The Terms of Service and Privacy Policy are not at /terms or /privacy, both of which return 404. They live at gmgn.ai/static/tos.html (last updated 6 December 2024) and gmgn.ai/static/privacy-policy.html (last updated 1 January 2025). Below is what those two documents said when we read them on 6 August 2026. This is a description of their contents, not an interpretation of them, and none of it is legal, regulatory or tax advice.
- Section 16.1 names the laws of the British Virgin Islands, and section 16.2 sends disputes to arbitration at the BVI International Arbitration Centre under BVI IAC rules, before a tribunal of three.
- No company is named in the document. The counterparty appears as "GMGN.AI", without a company number, registered address or list of officers, and section 19.5 directs questions, complaints and claims to a Telegram group and an X account.
- Neither document describes an identity-verification step. Reading the Terms, the privacy policy and the 68 documentation pages on 6 August 2026, we found no passage describing KYC and no passage in which a license or registration is claimed. What that absence means for GMGN, or for you as a user, is a question for a qualified lawyer in your own jurisdiction rather than one this page can answer.
- Section 5.2 asks you to represent that you are not in, under the control of, or a national or resident of Afghanistan, Cuba, Iran, North Korea or Syria, and not a person on UN, US OFAC or EU sanctions lists. The United States does not appear among the named countries. The clause is written as something you state about yourself, and we found no published description of how, or whether, GMGN verifies it. Whether you personally may use a service like this is governed by the law where you live, so ask a professional if the answer matters to you.
- Section 4.1 says you authorize GMGN to deduct fees directly from your wallet for each transaction, and reserves the right to change the fee schedule at any time, effective on posting.
- Section 8.14 lists front-running, wash trading and ramping among the things users agree not to do. We did not find an equivalent undertaking running in the other direction.
Then there is the documentation defect. The privacy policy carries another product's name throughout, branded "Meme Tracker": "This Privacy Policy describes the privacy practices of GMGN.AI ('Meme Tracker', 'we', 'us' or 'our')", with a data-rights contact link that reads literally https://t.me/Meme Trackerai.
Warning
Do not over-read that. A stale privacy policy is not evidence of misconduct, and we are not suggesting any. The reason to point at it is practical rather than legal: these are the documents you would be reading if you ever needed to rely on them, and one of them still carries a different product's name. Read both before you fund an account, and get advice from someone qualified if your situation calls for it.
So, is GMGN safe?
Safe against what. On the question of the operator taking funds, what we found as of 6 August 2026 is reassuring: no verified infrastructure compromise reported anywhere we looked, a 1,000,000 USDT top bounty tier run through HackenProof, an anti-MEV campaign fought in public, and compensation paid twice without users having to file claims. On the question of keeping access, the documentation points the other way: no exportable key, no seed phrase, no export on any chain including wallets you brought yourself, an EVM import that replaces the previous address, and a wallet whose only door is a Telegram account you do not control either.
Which points to one rule rather than an avoid-it verdict: keep only trading capital in a GMGN wallet, and sweep profits out to a wallet whose keys you hold. That habit prices in every risk above and costs you a withdrawal's worth of gas. If you are still deciding whether GMGN is the right terminal at all, our GMGN vs Photon comparison and the what is GMGN overview cover the product side, and the referral code page explains exactly who gets paid what, including the fact that referred users get no discount.
Read the custody terms before you fund anything
GMGN's docs and Terms of Service are linked throughout this page. Read both, then decide how much belongs in a wallet you cannot export. Our link pays us a referral commission and gives you no discount, because GMGN does not offer one.
Go to GMGNCite this page
These figures are free to quote. Copy the citation or the link below.
Plain-text citation
GMGNGuide. "Is GMGN Safe? Custody, Private Keys, and What You Actually Control." Published August 6, 2026, updated August 6, 2026. https://gmgnguide.com/security/is-gmgn-safe-custody-private-keysHTML link
<a href="https://gmgnguide.com/security/is-gmgn-safe-custody-private-keys">Is GMGN Safe? Custody, Private Keys, and What You Actually Control — GMGNGuide</a>Methodology and reuse
The custody policy, withdrawal holds and quoted policy language on this page are taken verbatim from GMGN's own documentation, its Terms of Service at gmgn.ai/static/tos.html, and its published bug bounty program. They were read from the GMGN TG wallet documentation on and re-verified against the live app. Exchanges change their schedules, so treat any figure older than that date as needing a fresh check — the date above is the one to compare against.
You may republish these figures with attribution and a link to https://gmgnguide.com/security/is-gmgn-safe-custody-private-keys.
Frequently Asked Questions
No. GMGN's wallet documentation states that all chains (SOL, EVM and Tron) are prohibited from exporting private keys, and that wallets imported from outside also cannot export private keys. Export was disabled around 19 March 2025. There is no seed phrase either. The documentation page is still titled 'Import & Export private key', which is why so many guides claim an export button exists. It does not.
GMGN's two published documents describe this differently, and this page does not resolve the legal question. Section 3.3 of the Terms of Service says you retain control over your private keys. The wallet documentation says all chains are prohibited from exporting private keys, including wallets imported from outside. The Agent API page describes a hosted wallet architecture where private keys are not stored locally. The multi-wallet page says logging in with Phantom creates what GMGN itself calls a multi-chain custodial wallet account. The bug bounty's top tier covers unauthorized access to GMGN wallets, funds or private keys. Read both documents, then treat the GMGN wallet as a hot trading account you cannot exit by key, and keep only trading capital in it.
No evidence for it turned up in this research as of 6 August 2026, and the reporting points the other way. An April 2025 analysis described GMGN users as the most sandwich-victimized cohort on Solana, at roughly 30.8 percent of sandwich attack profits inside a 30-day window covering more than 260,000 attacks. That analysis does not name its underlying dashboard, so treat those two figures as reported rather than independently reproduced. GMGN's co-founder publicly pressed Solana validators over leaked transaction data, shipped hardened anti-MEV routing in July 2025, and compensated sandwiched users. The accusation circulates about the whole terminal category, and no specific case naming GMGN as the front-runner surfaced in this research.
Check the published controls before assuming a freeze, because each of them looks like one. Withdrawals are web-only, the Telegram bot cannot withdraw at all, Google Authenticator 2FA is mandatory, funds only leave to whitelisted addresses, there is a 3-hour hold after the first whitelist setup or any whitelist change, and a 24-hour hold after re-binding Google Authenticator. The Max button also retains a small balance for rent and gas.
GMGN's Telegram wallet is bound to your Telegram account and there is no exportable key or seed phrase, so GMGN's documentation describes no key-based recovery path if that account is lost, banned or compromised. This is the sharpest practical argument for keeping only active trading capital in a GMGN wallet and moving profits out to a wallet whose keys you hold.
GMGNGuide is an independent reference published by a third party. It is not affiliated with, produced by, reviewed by, endorsed by or sponsored by GMGN.AI, GraceMatrix Technologies Limited, GMGN Labs Limited, or any of their affiliates. "GMGN" and GMGN's logo are trademarks of their respective owners and are used here only to identify the product this site writes about.
Disclaimer: Nothing on this site is legal, tax, financial or investment advice, and nothing here is a statement about whether any activity is lawful or how it should be taxed where you live. Trading memecoins carries a substantial risk of total loss. Verify anything that matters against GMGN's own documentation and consult a professional qualified in your jurisdiction. Most participants in these markets lose money, and past performance says nothing about future results. This site contains referral links, and GMGN pays us a share of the fees you pay without giving you a discount. See our disclosure for details.
Ready to Start Trading?
GMGN charges a flat 1% per trade across Solana, BSC, Ethereum, Base and Tron. Connect Telegram, fund the wallet, and set your slippage and priority fee before your first buy.
Open GMGN